

Bitget confirmed that losses from the hack recorded on September 24 continue to escalate and have already reached $387.5 million, cementing it as the largest theft from an exchange so far this year.
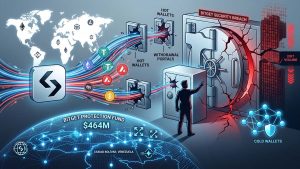
The attack did not involve the theft of private keys: the attackers infiltrated the backend system of Bitget’s wallet infrastructure and forged transaction data to deceive the internal authorization process itself, which approved the withdrawals as if they were routine operations.
Within 24 hours of the September 24 (UTC) incident: here is our further update as promised. Our investigation with Mandiant and SlowMist is ongoing — thorough forensic analysis takes more than 24 hours, and further findings will be shared as they become available. Three key…
— Gracy Chen @Bitget (@GracyBitget) September 25, 2026
The largest block of stolen assets corresponds to approximately 103 million XRP, equivalent to roughly $157 million. CEO Gracy Chen noted that the identified IP addresses match the VPN preferences used by a group linked to North Korea, and that the on-chain patterns align with techniques attributed to Lazarus Group, though authorship has not yet been officially confirmed.
Chen indicated that Bitget’s user protection fund, which exceeds $464 million, will cover the entirety of the losses, meaning customer balances will remain intact. Deposits and trading operations continued without interruption during the incident; only withdrawals were suspended as a precaution and will resume tomorrow.
Source: https://x.com/GracyBitget/status/2103487508147491014
Disclaimer: Crypto Economy Flash News are based on verified public and official sources. Their purpose is to provide fast, factual updates about relevant events in the crypto and blockchain ecosystem.
This information does not constitute financial advice or investment recommendation. Readers are encouraged to verify all details through official project channels before making any related decisions.