

TL;DR
- Bitget lost $351.6 million after a hack that compromised its wallet backend through forged transfers; no private keys were stolen.
- CEO Gracy Chen confirmed the unauthorized flow was stopped and that the $464 million User Protection Fund covers the total loss.
- The exchange suspended withdrawals as a precautionary measure. Technical teams are working on remediation of the compromised system.
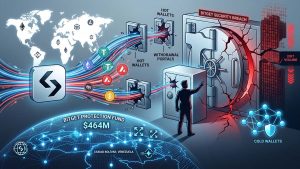
Cryptocurrency exchange Bitget suffered a $351.6 million hack following an exploit in the backend of its wallet infrastructure. Gracy Chen, CEO of the company, explained that the attackers did not steal the exchange’s private keys, but instead manipulated the system that prepares and validates transfer requests to deceive the authorization process.
“The attacker compromised a critical backend system within our wallet infrastructure, used it to forge transaction data and triggered our authorization process to move funds,” Chen wrote.
Live about Bitget Hot Wallet Incident on September 24, 2026 https://t.co/limZaY2pRf
— Bitget (@bitget) September 24, 2026
Forged Transfers: A Key Distinction
Chen described the attack as the digital equivalent of slipping forged withdrawal slips through a bank’s own teller window. The vault keys never left the building. Someone accessed the office that prepares the forms, fabricated legitimate-looking documentation and sent it through the same approval channel the system uses on a daily basis. To the validation process, everything looked like a normal operation.
The technical distinction between this method and private key theft is significant. When an attacker obtains a private key, they can keep signing new transfers indefinitely and drain funds without limit. In this case, the vector was different: an intrusion into the intermediary system that processes and presents orders, not into the cryptographic core that authorizes them. The unauthorized flow was definitively stopped, according to Bitget’s confirmation.
Bitget Covers Everything with Its Protection Fund
The vulnerability was detected at 18:31 UTC on September 24, when Bitget’s systems identified unauthorized transfers from some of the exchange’s hot wallets. The attack also reached the warm wallet layer, a semi-connected reserve that operates as a buffer between the automated hot wallets and offline storage. The exchange’s cold wallets remain intact.
Bitget confirmed that the company’s User Protection Fund exceeds $464 million and covers the loss in full. Deposits and trading remain active, although withdrawals were suspended as a precautionary measure.
The platform did not set a timeline for their resumption and clarified that the technical investigation is still ongoing. Multiple teams are working in parallel on the remediation and hardening of the compromised systems.