The debate over self-custody and bank custody of digital assets often appears as an ideological dispute. One side argues that control of private keys is the only legitimate form of ownership.
Another side argues that financial institutions must intermediate. The relevant technical question is not whether an individual can store a key. The relevant question is which legal, operational, and compliance structure each type of holder requires.
The position argued in this article is direct: institutional custody does not exist because clients are unable to use keys. It exists because funds, registered advisers, pension plans, and corporate treasuries operate under rules that self-custody does not satisfy.
Self-Custody: Technical Control, Not Governance
A private key allows signing transactions. An individual with a hardware wallet and a backup copy controls the asset. The model is sufficient for personal wealth, retail trading, and small treasuries. Self-custody eliminates counterparty risk from an intermediary. It also reduces dependence on a third party to authorize movements. However, technical control does not solve institutional problems.
It does not define who within an organization can approve a transfer. It does not establish segregation between client funds and operating funds. It does not generate auditable records for a regulator. It does not guarantee continuity if an employee loses a key or dies.
It does not manage inheritance, succession, or corporate recovery. For an investment fund, a single key is a single point of failure. Operational governance requires multiple approvals, separation of duties, and traceability. Self-custody, by design, concentrates control in the key holder. Concentration is acceptable for an individual. It is incompatible with a fiduciary mandate.
Qualified Custodian and Regulatory Mandate
In the United States, the SEC applies the Custody Rule to registered investment advisers. The rule requires client assets to be maintained with a qualified custodian. Self-custody does not meet the condition for many structures. The OCC has recognized crypto custody as a permissible banking activity, subject to AML/BSA and OFAC sanctions compliance. Other regulators have adopted similar approaches.
The result: a fund seeking to operate within the regulated system needs a custodian assuming legal responsibility. A bank does not compete with the private key of a client. A bank competes with other institutional custodians such as Coinbase Custody, Anchorage, or BitGo. Bank custody offers a compliance layer self-custody does not incorporate.
The layer includes customer identification, transaction monitoring, regulatory reporting, and sanctions controls. For an institution, such processes are not optional. They are a condition of existence.
Operational Governance and Internal Controls
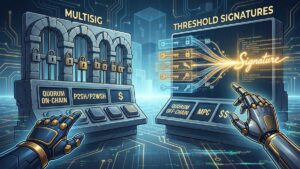
Custody of digital assets does not consist of storing a key in a vault. It consists of operating a control system. Banks use HSM (hardware security modules), MPC (multi-party computation), and cold storage with geographic redundancy. Keys are fragmented.
Transactions require multiple approvals. Trading and custody functions are separated. Records are designed for audit. Asset segregation prevents mixing client funds with entity funds. FTX showed consequences of ignoring controls. The FTX bankruptcy did not occur due to a crypto failure.
It occurred due to absence of governance, commingling, and deficient internal controls. A bank offering custody transfers practices from traditional securities custody to the digital environment. The transfer is not perfect. It covers gaps self-custody leaves open.
Counterparty Risk and Risk Transfer
Self-custody eliminates counterparty risk from an intermediary. It also concentrates operational risk on the holder. If the holder loses a key, no recourse exists. If an attack occurs, no responsible institution exists. If death occurs without a succession plan, assets become inaccessible. Bank custody inverts the equation. It introduces institutional counterparty risk.
The client depends on the solvency, controls, and continuity of the bank. In exchange, it reduces individual operational risk. The bank assumes custody, audit, and recovery responsibilities. It is necessary to clarify: crypto assets in bank custody are not covered by FDIC insurance.
They are not deposits. Some banks contract digital asset insurance. Policies have limits, exclusions, and conditions. Bank custody does not eliminate risk. It redistributes risk. For an institution, redistribution may be preferable to the burden of managing keys directly.
Institutional Demand and Bank Strategy
Banks offer custody not only for regulatory mandate. They respond to institutional demand. Family offices, hedge funds, wealth managers, and corporate treasuries want exposure to crypto assets without building their own infrastructure. They want statements, tax reports, integration with accounting systems, and a responsible counterparty.
Bank custody permits offering such services. It keeps assets within the banking relationship. If a client moves crypto assets to a native custodian, the bank loses visibility over part of the wealth. Custody permits recovering visibility and offering integrated services.
It also prepares banks for tokenization of traditional assets. Digital custody infrastructure serves tokenized securities, tokenized funds, and programmable payments. The strategy is not only defending the current business. It is building a position for regulated digital asset markets.
Criticisms and Limits of Bank Custody
Bank custody has valid criticisms. It introduces intermediaries into a system designed to reduce them. It can facilitate censorship or asset freezing by regulatory or judicial decision. It increases dependence on centralized institutions. It can create risk concentration if few custodians control a large share of assets. It raises transparency questions: how are reserves audited? how are keys proven? what happens in bankruptcy? The answer is not to deny bank custody.
The answer is to demand standards. Proof of reserves, independent audits, legal segregation, clear disclosures, and contingency plans. Self-custody remains necessary as an option. No regulatory framework should prohibit self-custody for individuals. The existence of self-custody does not invalidate institutional custody. They are models for different needs.
Coexistence of Models and Necessary Standards
The sector tends to present a false dilemma: self-custody or custody. Operational reality shows coexistence. An individual can hold own keys. A regulated fund can use a qualified custodian. A company can use MPC with internal approvals.
A bank can offer custody to clients not wanting to manage keys. Each model has costs and benefits. Self-custody maximizes sovereignty and minimizes counterparty exposure. Bank custody maximizes compliance and minimizes operational burden.
The decision depends on regulatory profile, risk tolerance, asset size, and audit needs. The sector should abandon ideological discussion and focus on standards. Interoperability, transparency, segregation, and audit are requirements for any custodian. The key question is not who holds the key. The key question is who responds when something fails.
The question “why do banks need crypto custody if clients can hold keys?” starts from a confusion. Banks do not need custody because clients cannot hold keys. Banks need custody because institutions require legal responsibility, operational governance, and regulatory compliance. Self-custody solves technical control. Bank custody solves accountability.
Both are compatible. Both have risks. Professional debate should not focus on eliminating one or the other. It should focus on building standards permitting each holder to choose with verifiable information. In an institutional market, custody is not a concession. It is infrastructure. Like all infrastructure, value depends on trust it can demonstrate.