TL;DR:
- The amount demanded by the attackers totals 6,000 Monero (XMR) tokens, equivalent to approximately $3 million as of September 16, 2026.
- The security incident exposed confidential information belonging to roughly 680 of the entity’s customers.
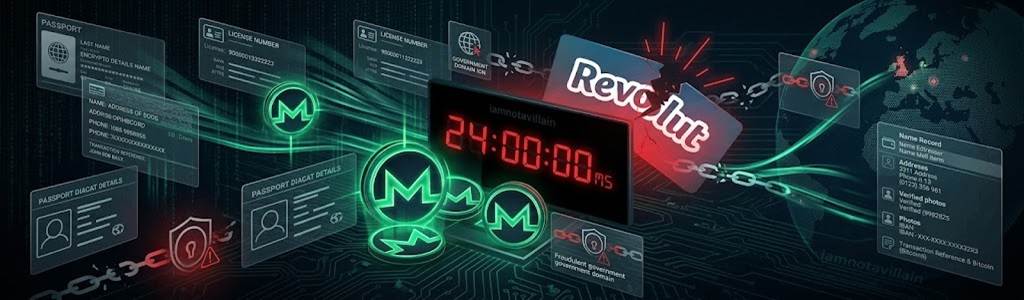
- The responsible group set a 24-hour ultimatum via a digital countdown timer on an external website.
The self-styled group “iamnotavillain,” linked to the British fintech data breach, reduced its ransom demand to $3 million under the threat of immediate sale. The Revolut hackers published a 24-hour countdown clock this Wednesday, September 16, as revealed by a Financial Times investigation.
The financial demand requires the transfer of 6,000 units of the cryptocurrency Monero (XMR). The digital asset was selected by the cybercriminals due to its privacy and anonymity cryptographic protocols.
According to the Financial Times report, the attackers claimed they will sell the files of 680 users to criminal networks if the stated amount is not paid. A 60-second screen recording provided to the newspaper showed passports, driver’s licenses, and complete banking records.
Revolut stated officially that it has not received any direct demand from the extortionists. A company spokesperson confirmed that core infrastructure and primary databases suffered no unauthorized access.
Institutional Impersonation and Scope of Compromised Data
The breach occurred via a fraudulent information request originating from a legitimate government domain. Compliance staff processed the request before identifying the identity spoofing.
Official company disclosures indicated that leaked data includes names, residential addresses, phone numbers, and identity verification photographs. The cache also comprises IBAN numbers, account opening dates, and account statements referencing Bitcoin transfers.
The attackers told the Financial Times that they used on-chain analytics to target customers with significant digital asset holdings. Prior reports by on-chain investigator ZachXBT suggest that the affected accounts corresponded to high-net-worth profiles.
The company blocked the domain leveraged for the deception and formally alerted law enforcement authorities. The UK Information Commissioner’s Office (ICO) maintains an open formal investigation into the matter.
The extortionists’ ultimatum expires this Thursday, September 17, 2026. UK and European Union regulators have scheduled supervisory hearings on the incident toward the end of the third quarter of 2026.