

TL;DR:
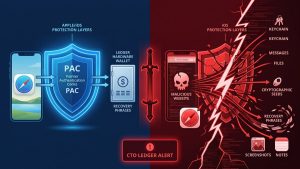
- CTO Alert: Charles Guillemet, Ledger’s Chief Technology Officer, publicly recommended that users avoid storing recovery phrases and private keys on iPhone devices.
- iOS Vulnerability: The warning responds to a Binance report regarding the worse_query flaw, which potentially allows malicious apps to access local files of other apps on recent versions of iOS.
- Preventive Measures: Industry guidelines suggest uninstalling unverified software, updating the operating system, and migrating funds to clean devices upon any suspicion of compromise.
Ledger CTO Charles Guillemet addressed digital asset holders to warn them to avoid storing critical wallet information on iPhone devices. The executive made this warning public following a security alert issued by the Binance exchange regarding a vulnerability detected in Apple’s iOS operating system.
Unfortunately this kind of vulnerability used to be very expensive and reserved to high potential attackers. Their cost is trending towards zero and are now exploitee at scale.
Simply don't store any valuable in your mobile, especially not your crypto seeds… https://t.co/8SReu7k5QU
— Charles Guillemet (@P3b7_) November 10, 2026
The Ledger executive used his official X account to post that security flaws allowing the extraction of confidential data are becoming increasingly accessible to cyber attackers.
The Technical Context of the iOS Vulnerability
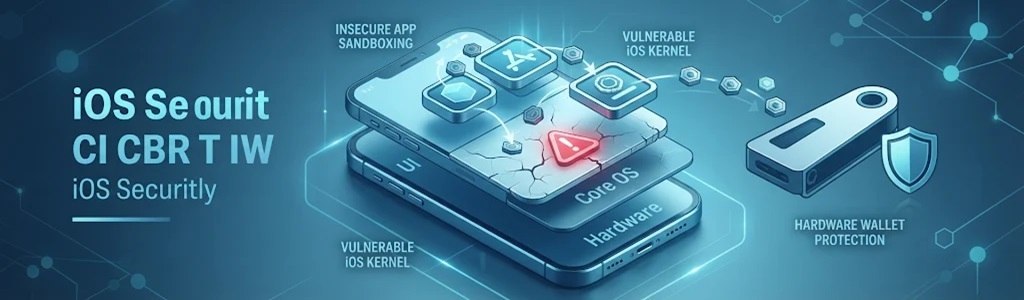
The Binance team revealed data indicating that the identified flaw, dubbed worse_query, potentially allows malicious applications to gain unauthorized access to files from other apps installed on the same mobile device. Exchange specifications indicate that this security issue affects specific versions of Apple’s mobile operating system.
Technical documentation suggests that private keys, login credentials, and digital wallet recovery phrases could be exposed because this data is usually stored in accessible local files. Given this scenario, Ledger’s management emphasized the need to exercise extreme caution when handling mobile devices for the custody of financial assets.
“Simply do not store any value on your mobile device. Especially not your cryptocurrency recovery phrases,” Guillemet warned via his official post.
Security Recommendations and Recent Background
In response to the technical incident, guidelines issued by exchanges suggest uninstalling applications obtained from unverified sources, immediately updating operating systems, and strictly restricting the installation of unauthorized software. Likewise, transferring funds to new wallets configured on clean devices is recommended in case of any suspicion of compromise.
Apple, for its part, released security updates at the beginning of November, although industry reports indicate that the full scope of the patch against the reported attack vector is still being evaluated. To date, consulted sources have not confirmed massive cryptocurrency thefts directly linked to this specific exploit.
This warning from the hardware wallet company adds to other security events reported in the sector over recent weeks, including previous incidents related to the physical device supply chain in the Asian market. The company continues to urge the community to prioritize the use of dedicated hardware disconnected from the internet for the long-term management of private keys and cryptocurrency funds.