

News
CertiK Discovers Hidden Malware Targeting Crypto Developers
CertiK identifies malicious code hidden in a Hardhat configuration file linked to the PolinRider campaign and targeting cryptocurrency developers.

Key points
- Blockchain security firm CertiK identified a malicious script hidden inside a Hardhat configuration file during a smart contract audit.
- The concealed code used Ethereum transactions to locate remote servers and download additional payloads without requiring an on-chain deployment.
- Analysts linked the loader to a software supply chain campaign named PolinRider, focused on compromising computer development environments.
CertiK reported the discovery of malicious code camouflaged within a Hardhat configuration file, commonly used by engineers in their compilation and testing routines. The official report this Tuesday, November 17, indicates that the disruptive element was not found in the analyzed smart contracts, but rather in the workflow tools themselves, which could expose credentials and deployment keys if environments are executed normally.
A smart contract can pass every test while its development environment is compromised.
During an audit, we uncovered a hidden malware loader linked to PolinRider, capable of exposing developer credentials through routine Hardhat commands.
Full analysis↓ https://t.co/pgfCeGPC84
— CertiK (@CertiK) November 17, 2026
Specialists detailed that the script was concealed using a wide whitespace within the file, pushing it away from the visible area of conventional editors. Since the Hardhat tool processes its configurations as JavaScript, lines located beyond the traditional exported module can be activated automatically when loading the file, without the user noticing its presence during a superficial code review.
Operating mechanism and remote servers
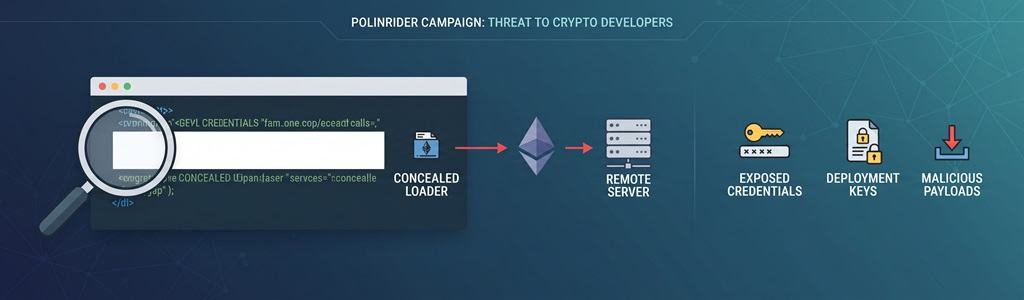
The technical investigation conducted by the company indicates that the loader incorporated functions to decrypt and execute instructions downloaded from external servers. To avoid direct modifications in the infected repository, the malicious software used specific Ethereum transactions to query updated server addresses dynamically.
According to the official report, the system integrated alternative connection endpoints and fallback mechanisms for network failures. After establishing contact with the external server, the program downloaded encoded scripts and proceeded to local execution via Node.js processes, including hidden instances capable of remaining active even after the developer’s original command finished.
Likewise, the data gathered by CertiK indicates that the code suppressed usual error messages to hinder detection during daily tasks. Experts explained that this attack vector is compatible with the characteristics of the PolinRider campaign, previously identified for targeting vulnerable links in the cryptocurrency software supply chain.
Implications for project security
The report warns that the compromised configuration processed environment variables prior to the activation of the concealed script. This granted the external code permissions over private deployment keys and other accesses stored on the affected machine, increasing the risk of confidential information leaks.
The security firm clarified that the subsequent removal of the malicious line does not reverse previously executed processes nor guarantee system integrity. For this reason, potentially affected teams were recommended to preserve activity logs, isolate compromised computers, and proceed with credential rotation from clean and verified IT infrastructures


