TL;DR:
- On August 31, 2026, an attacker extracted approximately $1.26 million in digital assets across 26 transactions on the Radix network.
- Validators coordinated the deliberate withdrawal of their stake to halt consensus for 10 consecutive days until a security patch was deployed.
- The vulnerability was introduced during a code refactoring in June 2023 and bypassed an external security audit conducted by Zellic in 2024.
A 3-year-old bug drained $1.3 million after breaching the execution engine of the Radix network on August 31, 2026. The information was confirmed by the Radix Foundation on Thursday, September 17. They added that the incident forced validators to completely halt block processing for ten days to prevent the hacker from compromising additional vaults across the ecosystem.
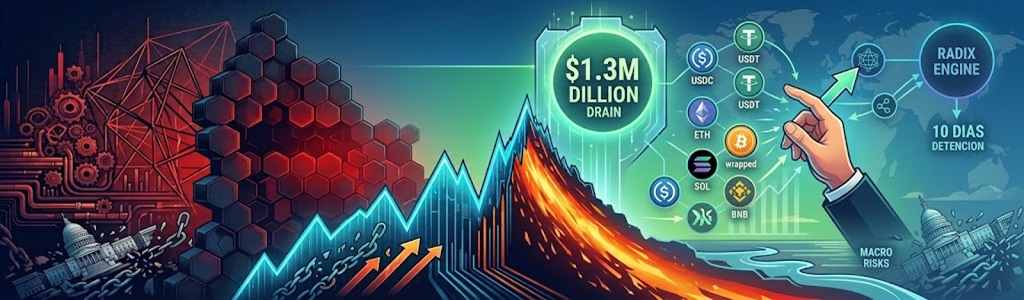
On-chain records show that the hacker executed 26 transactions between 16:02 and 16:57 UTC on August 31. During that operational window, the malicious address extracted 458,915 USDC, 72,420 USDT, 61.08 ETH, 6.35 wrapped Bitcoin, 536.16 SOL, and 32.91 BNB, amounting to an initial valuation near $1.26 million at market prices on that date. The entity also drained 13,000 XRD tokens from a vault to cover network transaction fees.
The attacker routed the funds through the Hyperlane bridge toward Ethereum, BNB Chain, and Solana to liquidate them for ETH, according to Radix’s official report. Technical documentation indicates that the bridge protocol operated as intended, given that the funds exited after being improperly released at the local execution layer without any compromise of private keys.
The investigation determined that the breach originated during a code cleanup carried out by RDX Works in June 2023 on the Radix Engine. This component manages execution and ownership verification across the network’s vaults.
Execution Layer Flaw and Consensus Halt
Security firm Zellic audited the Radix protocol in 2024 without detecting the missing authorization boundary checks, according to details in a market report. The flaw allowed a malicious contract to invoke standard withdrawal functions using the internal address of any external vault, bypassing cryptographic signature verification from legitimate holders.
Researchers concluded that the bug potentially exposed every vault on the network, threatening the protocol’s total liquidity. Faced with this scenario, validator node operators intentionally withdrew sufficient stake to halt Byzantine consensus and freeze ledger activity starting on the afternoon of August 31.
The operational shutdown lasted for more than ten consecutive days while developers prepared the fix. Community records indicate that transactions returned to normal on September 11, once the patch blocking unauthorized references was successfully deployed.
The incident caused secondary distortions across decentralized liquidity pools within Radix. The abrupt removal of bridged assets threw trading pairs out of balance, enabling third parties to withdraw millions of XRD tokens at skewed rates prior to the network pause.
Radix announced that it will introduce additional regression testing and formalize the emergency procedures executed by validators. The foundation expects to publish updated audits covering the authorization logic before the close of the fourth quarter of 2026.