

TL;DR:
- A malicious script injected through a third-party vendor drained $2.7 million from 726 wallets on October 29, 2026.
- The platform rolled out a total compensation package of $3.9 million to cover both the drained assets and collateral losses caused by the operational downtime.
- As of the morning of October 30, 2026, 689 accounts have already received their full funds, leaving 37 cases under individual verification.
Decentralized prediction market Polymarket will refund $3.9 million to affected traders after detecting a malicious script on its web interface on Thursday, October 29. The attack vector did not breach the underlying smart contract infrastructure, focusing instead on the web layer through a compromised third-party vendor.
✅ 689 of 726 affected wallets have been refunded in full. The remaining 37 are being paid as each is verified.
We're also going further. Traders who lost money during our trading pause, or whose positions were taken, are covered too: $1.19M to 5.5K wallets, starting today.
In…
— Polymarket Traders (@PolymarketTrade) October 30, 2026
At 18:05 UTC that same Thursday, the platform temporarily halted order execution and shifted its matching engine to cancel-only mode to contain the incident.
According to the breakdown shared through official channels, attackers directly drained nearly $2.7 million from 726 user wallets. The total restitution program amounts to $3.9 million because the company chose to cover collateral trading losses as well. These additional amounts account for positions that became locked or suffered unexpected liquidations during the technical downtime window.
By Friday, October 30, platform records indicated that 689 wallets had received a complete refund of their balances without requiring any extra procedures. The remaining 37 accounts remain under manual review to verify ownership and determine the exact amount before processing the final payouts.
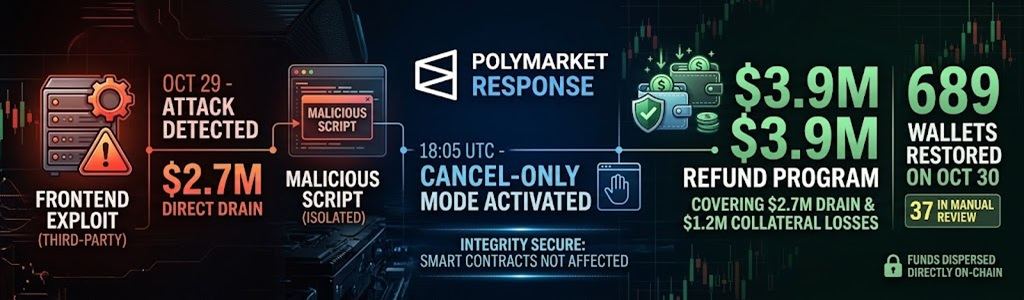
Interface-Layer Attack Vectors and Technical Response
Preliminary technical analysis showed that the exploit originated in a third-party asset optimization library loaded on the international site. That legitimate snippet was replaced with a drainer script capable of interacting with active user sessions.
According to technical metrics tracked by on-chain analytics firms like Arkham, the stolen assets were primarily swapped into POL and pUSD tokens before dispersing across the network. Because the script ran strictly inside client browsers via unauthorized calls to exchange contracts, Polymarket’s core settlement contracts maintained full cryptographic integrity.
This vector aligns with an earlier breach documented in June 2026, where a frontend code injection compromised roughly $3 million in user funds. The October 29, 2026 incident also marks the second interface exploit targeting prediction platforms within the same week, following comparable attacks reported across competing protocols.
Security intelligence firms immediately warned about malicious copycat domains and fraudulent links spreading across social platforms under the guise of refund claim portals. Polymarket developers stressed that all restitution payments are issued directly on-chain to original user addresses, without asking users to connect to third-party dashboards or sign new contract allowances.
The platform has progressively restored regular market operations after isolating the compromised external dependency. The restitution review for the final 37 accounts and the release of an exhaustive post-mortem forensic report are slated for completion during the first days of November 2026.