The debate around crypto custody in institutional settings often presents two positions. One side defends self-custody as a non-negotiable principle.
The other side argues that institutions require regulated custodians. The relevant question is not whether an institution can store a private key. The relevant question is what operational governance structure an institution requires to manage digital assets under auditable standards.
A fund that manages crypto positions does not face the same problem as an individual who holds a personal wallet. The difference is not solely the amount, although amount matters. The difference lies in the fiduciary, regulatory, and operational obligations that apply to the entity.
A collective investment vehicle must demonstrate segregation of assets, transaction traceability, separation of functions, and business continuity under adverse events. A private key stored on a hardware wallet does not resolve any of those requirements.
The Real Problem: Operational Control and Separation of Functions
Institutional self-custody presents a structural problem that storage technology does not solve. If one person inside the organization controls the private key that provides access to assets, operational risk concentrates to a disproportionate degree.
The disappearance of that person, the loss of a seed phrase, or the compromise of credentials produces an irreversible event. Native blockchain assets cannot be reversed by a central administrator after leaving a wallet.
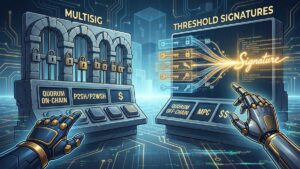
Technical solutions exist. Multisignature schemes, multi-party computation (MPC), and hardware security modules (HSM) distribute control among multiple parties. However, implementation of those mechanisms inside a financial institution requires access policies, approval procedures, audit logs, and disaster recovery plans.
Technology alone does not constitute a governance framework. An institution that adopts multisignature without defining who approves which transaction, under what conditions, and with what documentation has not solved the custody problem. The institution has moved the problem to a different layer.
The Federal Reserve, the FDIC, and the OCC have identified key loss or compromise as one of the central risks that banks must manage when providing custody services. The identification is not accidental. It reflects that risk is not exclusively technical. Risk involves internal controls, segregation of duties, and business continuity.
The Regulatory Framework as a Determining Factor
The OCC published guidance in 2025 that authorizes national banks in the United States to provide crypto custody and execution services, including through approved sub-custodians. The guidance does not create an obligation for institutions to use banks as custodians. The guidance establishes a legal certainty framework so that banks can offer the service.
The relevance of the framework lies in the obligations that apply to certain investment vehicles. Collective investment funds may require qualified custodians, independent recordkeeping, periodic audits, and segregation of client assets from assets of the managing entity.
Banks already operate infrastructure designed to meet those requirements. A fund that chooses self-custody must build that infrastructure from zero or accept that the fund cannot meet applicable standards.
Segregation of assets is a concrete example. In an institutional self-custody scheme, fund assets and assets of the managing entity may end up under control of the same persons, in the same wallets, or in linked wallets. Effective separation requires organizational controls, not only technical controls. A custody bank offers that separation as part of its operating model.
Custody Does Not Equal Absence of Risk
Bank custody of crypto assets does not eliminate risk. A custodian can suffer a cyberattack, an operational failure, or a third-party breach. The difference lies in the nature of risk and in the existence of mitigation mechanisms.
An institutional custodian operates with insurance policies, recovery procedures, role-based access controls, and auditable reports. An institutional self-custody scheme can incorporate some of those elements, but doing so requires investment in infrastructure, specialized personnel, and formal processes. For many institutions, that investment is not viable or is not part of their core activity.
Custody converts a problem of indefinite nature—protecting a private key indefinitely—into a managed system of controls, approvals, insurance, reporting, and accountability. The conversion has a cost. The conversion also has value for institutions that operate under regulatory frameworks requiring levels of control that simple self-custody does not provide.
The Tension with Original Principles
The crypto sector was built on the premise that control of private keys equals control of assets. Institutional custody introduces an intermediation layer that moves away from that premise. The tension is real and should not be ignored.
However, institutional adoption of crypto assets does not advance exclusively on principles. Institutional adoption advances on operational and regulatory requirements. Institutions that manage third-party capital operate under obligations that cannot be resolved through simple possession of a key. The relevant question is not whether bank custody contradicts the original principles of the sector. The relevant question is whether institutions can meet their obligations without bank custody.
The answer, for a significant segment of the institutional market, is that institutions cannot. Regulated custody offers a framework that institutional self-custody does not provide immediately. That does not invalidate self-custody as an option for individuals or for entities that decide to assume the costs of building their own infrastructure. The answer establishes that, for certain actors, bank custody responds to a concrete operational need.
The Cost Structure of Custody Models
A comparison of custody models requires an examination of cost structures. Self-custody carries direct costs: hardware security modules, redundant key storage, insurance, specialized staff, audit procedures, and legal review. Bank custody carries service fees, minimum balance requirements, and contractual constraints.
The cost comparison is not universal. A small fund with limited assets under management may find bank custody more expensive per unit of risk mitigated. A large fund with complex approval requirements may find self-custody more expensive when all operational costs are included.
The decision also involves counterparty risk. A custody bank introduces a counterparty. Self-custody eliminates a custody counterparty but introduces key management risk. Neither model eliminates risk. Each model allocates risk to different parties and different processes. An institution must determine which allocation aligns with its fiduciary duties and its regulatory obligations.
Operational Scalability
Self-custody does not scale linearly with assets under management. A small position can be managed with a single hardware wallet and a documented seed phrase.
A large position requires multiple approvals, geographic distribution of key shares, transaction limits, time locks, and audit trails. The operational complexity increases with the number of counterparties, the number of transactions, and the number of regulatory jurisdictions involved.
Bank custody provides scalability through existing infrastructure. The bank already operates segregated accounts, approval workflows, audit departments, and compliance functions. The marginal cost of adding a crypto custody client to that infrastructure is lower than the cost of building equivalent infrastructure from zero. The scalability argument does not apply to every institution. The argument applies to institutions that lack the scale to justify a dedicated custody operation.
Regulatory Arbitrage and Jurisdictional Differences
Crypto custody regulation varies by jurisdiction. The OCC guidance applies to national banks in the United States. The European Union has adopted the Markets in Crypto-Assets (MiCA) regulation, which includes custody requirements.
Other jurisdictions have different frameworks. An institution that operates across multiple jurisdictions must comply with the strictest applicable framework. Bank custody can simplify compliance when the bank already operates under multiple regulatory regimes. Self-custody requires the institution to demonstrate compliance independently in each jurisdiction.
The simplification is not absolute. A bank custodian remains subject to its own regulatory obligations. The bank may be prohibited from serving certain clients or certain asset types. The bank may be required to freeze assets under specific legal orders. An institution that uses bank custody accepts those constraints as part of the service.
The discussion of crypto custody in institutional settings requires precision. The debate is not between self-custody and bank custody as equivalent options.
The debate is between different models of operational governance for digital asset management. Institutional self-custody is viable for entities that build the necessary infrastructure. Bank custody is viable for entities that require a framework of controls, segregation, audit, and regulatory compliance that already exists in the traditional financial system.